네트워크 포렌직 퍼즐 #1 풀이입니다.
http://forensicscontest.com/2009/09/25/puzzle-1-anns-bad-aim
1. . What is the name of Ann’s IM buddy?
Sec558user1
SSL
패킷을 [TCP Follow Stream] 을 통해 뽑아보면 아래와 같이 대화명을 확인할 수 있다.
- What was the first comment in the
captured IM conversation?
Here's the secret recipe... I just downloaded it from the file server. Just copy to a thumb drive and you're good to go >:-)
역시 마찬가지로 [TCP Follow Stream] 메뉴를 통해
확인할 수 있다.
- What is the name of the file Ann
transferred?
recipe.docx
마찬가지다...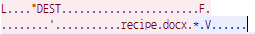
4**. What is the magic number of the file
you want to extract (first four bytes)?**
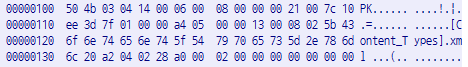
50 4b 03 04,
0×504B0304
Filter : tcp.port == 5190
위와 같이 필터를 설정 후 나오는 패킷을
[TCP Follow Stream] 기능으로 보면 아래와 같이 확인할 수 있다.
5**. What was the MD5sum of the file?**
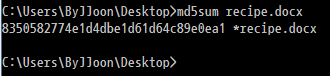
8350582774e1d4dbe1d61d64c89e0ea1
TCP Follow Stream 에서 처음 받은 데이터를 제외하고 나머지 데이터로만 파일을 만들면 MS Word 파일을 확인할 수 있다.
6**. What is the secret recipe?**
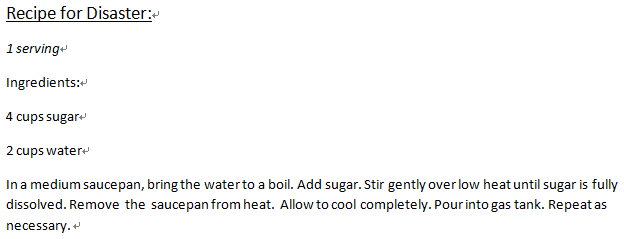
첨
부파일의 내용은 아래와 같다.